This guide explains how to responsibly interpret “Nilo oliveria. 71992365632” in a business context, covering identity checks, verification methods, and safer outreach practices. Objectively, the keyword string resembles a name plus a numeric identifier; without verified documentation, it should not be treated as proof of affiliation. The article outlines conditions, step-by-step due diligence, and practical requirements.
If you encounter “Nilo oliveria. 71992365632”, the safest and very professional approach is to treat it as an unverified identifier until you confirm context through reliable records. In practice, this means: verify the person or entity, validate whether the number is connected to legitimate services, and document what you can substantiate. This guide is written to help you proceed with appropriate due diligence—especially when the information appears as a name followed by a long numeric string.
From an industry perspective, the core risk in handling such identifiers is not “data scarcity,” but misassociation: confusing a contact detail for proof of ownership, employment, or authorization. A numeric sequence may represent anything from an internal reference to a phone/account identifier. Therefore, professional workflows emphasize verification, consent, and transparency before you act on the information.
It is also important to note that strings like this often travel through many systems: copied from messaging apps, pasted from forms, scraped from directories, or included in marketing content. Any one of those paths can introduce errors, outdated information, or deliberate manipulation. Even if the string is correct, the question remains whether the person who provided it is authorized to represent the relevant party or whether the contact leads to the claimed counterpart.
The provided keywords—Nilo oliveria. 71992365632—appear to combine:
In data-handling and compliance-oriented work, this pattern is common: a name is paired with a contact-like number to facilitate communication or referencing. However, format alone cannot confirm legitimacy. Verification requires external corroboration—such as official registries, documented business websites (without assuming ownership), prior correspondence under consent, or confirmation from reputable directories.
Because no additional supplier, pricing, or location-specific information was provided in your input, this article intentionally avoids inventing details. Instead, it focuses on a robust method you can apply regardless of industry—sales, procurement, customer support, leasing, real estate services, or logistics—whenever a similar identifier is encountered.
Think of the string as a hypothesis, not a fact. “Nilo oliveria” might be the person’s name, but it might also be an organization name, a contact alias, or even part of a longer record where punctuation was lost. The digits might be a phone number, a WhatsApp number, a messaging service identifier, an account number, or an internal ticket reference. Your job is to reduce uncertainty by confirming, not by guessing.
When you see “Nilo oliveria. 71992365632,” treat it like a starting point, not an endpoint. A professional approach reduces the chance of contacting the wrong party or acting without authorization.
Key actions typically include:
For organizations working under regulated environments (procurement, consumer finance, healthcare-adjacent operations, B2B contracting), recordkeeping and verification steps are especially important. Even outside regulation, these habits improve service quality and reduce disputes.
Also consider communication channel validation as its own step. If the digits correspond to a mobile number, confirm whether the person responds as the same entity across channels: for example, email (from a domain you can verify), website contact page, and business email signature. Consistency across channels makes it more likely the contact is genuine and reduces the risk of engaging with someone impersonating a brand.
Across customer engagement, procurement coordination, and vendor onboarding, very errors come from one of these causes:
In many real-world cases, even legitimate vendors can accidentally mislead due to internal changes: a staff member might have new contact details, but the website still shows an older number, or vice versa. That is why verification should include confirming that the specific number you have is the currently active channel for the claimed party.
There is also a practical error called reverse confirmation failure: you confirm that a phone number exists, but you fail to confirm that it belongs to the person/entity you intend to transact with. For example, the number might answer the phone but still belong to a receptionist, a third-party call center, or someone unauthorized to act on contracts. The goal is not merely reachability; it is rightful association.
Finally, there is the risk of time-based inconsistency. People change roles and contact details. A record that was accurate months ago may not be accurate today. Professional workflows therefore check for “freshness”: recent website updates, recent communication history, current status on official pages, and the ability to confirm details in the present.
If you plan to contact the person or entity associated with 71992365632, consider a concise, non-accusatory message that requests verification rather than demanding proof immediately. Example structure:
This approach aligns with common customer service standards: it reduces friction and increases the likelihood that the other party will respond constructively.
Here is a neutral outreach example you can adapt:
“Hello, my name is [Name]. I’m contacting you because I found the identifier ‘Nilo oliveria. 71992365632’ in [context]. Could you please confirm whether you are representing [company/person] and whether this number is the correct contact for [topic]? If possible, please share a verifiable business identifier or the official contact page/email associated with your organization. Thank you.”
Notice what this message does:
In professional practice, clarity and respect are often more effective than heavy-handed requests. Fraudsters sometimes become defensive; legitimate vendors usually respond with straightforward verification and supporting documentation.
Because your additional information section was blank, the article provides a comprehensive supplemental module as a comparison table, followed by a step-by-step guide and conditions/requirements—positioned slightly later, as requested.
Before that module, it is useful to clarify what “verification” practically means. In many industries, verification includes at least one of the following: official registration, documented authority, consistent contact routing, or corroboration from reputable directories and official channels. Relying on format alone is not considered sufficient by professional onboarding practices.
Verification should also be proportionate to risk. For low-risk interactions (basic inquiry), you might only ask for confirmation and use cautious messaging. For higher-risk interactions (payments, contracts, data access), you should require stronger proof: official documentation, agreement terms, and checks against authoritative sources.
Even if you believe the identifier is legitimate, you should manage risks:
These practices reflect established risk principles used in vendor onboarding and consumer protection guidance across industries.
To make risk management more concrete, consider three common failure modes in identifier-based engagements:
A verification process—done correctly—reduces the likelihood that you fall into any of these patterns. The best defense is to require that the other party can prove connection to the claimed identity, and that they can do so without demanding that you lower your standards.
Also remember: refusal to verify is a signal, but so is forced urgency. Fraudsters often push fast decisions (“send the deposit now,” “don’t wait for contract,” “the paperwork is delayed”). If you observe urgency combined with a refusal to provide basic documentation, pause and elevate your checks.
Below is a supplemental module that organizes verification methods into a comparison table, a practical step-by-step workflow, and clear conditions/requirements. Note: no location-specific substitution is needed here because the provided keywords did not include a city or country name.
| Verification Aspect | What to Check | Why It Matters | What Good Looks Like |
|---|---|---|---|
| Source of “Nilo oliveria. 71992365632” | Where you found it (e.g., inquiry form, prior thread, listing) | Reduces misattribution risk | You can explain the origin and context clearly |
| Identity Association | Is the name consistently linked to the same number and claims? | Prevents confusing different individuals/entities | Multiple consistent references with credible context |
| Authorization | Is the person able to negotiate or represent a business? | Avoids unauthorized commitments | Confirmed role, documented authority, or verifiable business status |
| Communication Channel Validation | Is 71992365632 reachable and corresponding accurately? | Improves reliability and reduces fraud exposure | Consistent replies aligned with the claimed counterpart |
| Transaction Clarity | Scope, timeline, and expectations | Prevents misunderstandings and disputes | Clear terms in writing before any commitments |
| Request for Sensitive Data | Does the counterpart ask for payment data or credentials too early? | Helps detect phishing or social engineering | They request appropriate info only after verification and written terms |
| Consistency Across Documents | Do details match across invoice, email domain, website, and contract? | Identifies mismatched identities or forged materials | Documented details align consistently |
| Third-Party Corroboration | Can you verify using authoritative or reputable directories? | Adds independent confidence | Corroboration supports claimed identity or business existence |
| Response Behavior Under Verification | How do they react to reasonable verification questions? | Assesses legitimacy and reduces compliance risk | They cooperate calmly and provide documentation |
To further strengthen due diligence, professionals often use a lightweight “gating” approach. That means they separate the process into stages (for example: contact stage → basic verification stage → contract stage → payment stage). Each stage has minimum proof requirements. With that structure, you avoid a common mistake: letting early contact progress into payments or commitments without appropriate checks.
It can also help to define “what you consider acceptable proof.” For instance, acceptable proof might include: a contract signed by a named representative, a business registration number matched to a public record, a website domain that confirms the organization identity, or an official email address. The exact standard depends on your internal policies and the risk of the transaction.
If you are an individual consumer rather than a company, you may still apply these principles in a scaled manner: ask for written confirmation, request proof of identity when stakes are high, and keep communications in channels that preserve records. Even simple steps like asking for an invoice template or business address can help separate legitimate operations from unverified claims.
Capture details such as the platform (email, SMS, social media, marketplace listing), the date, and the specific message or field where the identifier appeared. If multiple strings appear (variants of the name or different digits), record those too. Differences can reveal copied data, formatting errors, or deliberate attempts to obscure identity.
Keep initial questions simple. You want cooperation, not confrontation. The aim is to clarify: who they are, who they claim to represent, and whether the number corresponds to that representation.
For B2B contexts, reasonable documentation might include: business registration details, official website contact information, or a contract template with company identification. For personal contexts, request proof that matches the claimed identity (for example, consistent name and appropriate role context) without demanding unnecessary sensitive information upfront.
Consistency includes spelling of the name, matching contact details, and stable descriptions of services or products. If details shift significantly, treat it as a risk indicator. Track what changes and when you observed them.
Write down the scope: deliverables, timeline, service level expectations, and any constraints. This step prevents “vague agreement” situations that can later create disputes where it becomes hard to prove what was agreed.
Use a contract, purchase order, or written quotation that includes business identifiers and signatory details. If you communicate via email, ensure the written agreement is saved in your records. In more formal environments, procurement systems and audit trails should be used.
“Standard policy” matters. It should define whether you require additional checks such as vendor onboarding forms, internal approvals, or compliance screening. Even a legitimate counterpart may still fail internal compliance requirements.
Documentation is not bureaucracy; it is protection. In a dispute, your records show due diligence and help your organization respond appropriately. At minimum, save: the source of the identifier, the verification steps performed, and the written agreement that followed.
As a practical addition, you can use a simple checklist before moving to any payment step:
If “Nilo oliveria. 71992365632” appears in a marketplace listing (for example, a classifieds site or an online shop), you should treat it as an unverified lead until you confirm:
A professional approach includes checking the seller’s history, reviews, and ability to provide documentation. If the seller refuses to provide invoice details or asks you to pay outside the platform in a way that avoids records, that is a red flag.
If someone sends you “Nilo oliveria. 71992365632” without context, you should request context and purpose before sharing any data. A legitimate business should be able to explain why they contacted you, what they want, and what the next step should be.
In such cases, you can also confirm independently whether the business exists and whether their contact methods match. Be wary if the sender:
If the identifier appears in a procurement workflow, treat it as a required field that needs validation. Many organizations maintain vendor onboarding procedures such as:
Even when the number appears in your system, you still validate. Data in a form is only as reliable as the person who entered it. Your onboarding should treat it as an input rather than a confirmation.
If you receive an invoice or quotation that includes the string “Nilo oliveria. 71992365632,” do not treat it as automatic proof. Instead, verify that:
Invoices are often forged with realistic formatting. Verification should therefore focus on identity and authority, not just presentation.
In real estate and leasing, the risk of fraud can be higher because payments and sensitive identity documents are common. If the identifier appears as a contact for a landlord, agent, or property manager, you should:
Be cautious if the counterpart requests deposits without a signed agreement or asks you to transfer money to an account unrelated to the property management entity. Legitimate processes typically align payment destination with formal contract documents.
No. A name combined with a numeric identifier can be a lead, not proof. Verification should include corroboration of identity and authorization through credible sources or documented confirmation.
Ask whether 71992365632 is the correct number for the specific person/entity you intend to contact, and request role or business confirmation. If relevant, ask for a verifiable business identifier and a written confirmation of the service scope.
In professional practice, you should not. Share minimal necessary information and avoid payment or sensitive data until authorization, scope, and terms are confirmed in writing.
Formatting is not a reliable validation method. It may be copied, edited, or misattributed. Treat the string as unverified data until confirmed.
That’s a warning sign. A credible counterpart can typically explain how they represent their organization and confirm the basics of their authority. If they cannot, you should pause and consider alternative suppliers.
Yes. The principles—verification, consent, clarity, and recordkeeping—apply broadly, including customer support, scheduling services, partnerships, and any transaction involving an individual or organization.
That inconsistency can indicate an alias, a transcription error, or a situation where the contact is not authorized to represent the named entity. You should treat it as a verification failure and ask for clarification, written role confirmation, and supporting documentation before proceeding.
Fast document provision is generally a positive sign, but it does not automatically guarantee legitimacy. You still need to check consistency (spelling, identifiers, addresses, signatory names) and ensure the documents align with independently available information. For higher-risk transactions, consider additional internal compliance checks.
If you’re dealing with a transaction that requires documentation (contracts, procurement, scheduled services), inability or unwillingness to provide basic verification is a risk indicator. Legitimate businesses usually can provide at least some verification such as official business identity, terms of service, or contract templates.
Use a multi-factor verification approach: confirm name, role, organization, official website contact, and agreement signatory. A shared line (reception or call center) can be legitimate, but you must still verify who has authority to commit and who will be responsible for the work.
This article avoids unverified numeric claims, pricing figures, or supplier assertions because none were provided. For risk-management principles aligned with widely adopted practice, readers may refer to general guidance from:
Because no specific jurisdiction was supplied, this guide stays general and emphasizes verification steps rather than jurisdiction-specific legal conclusions.
When you encounter Nilo oliveria. 71992365632, the professional takeaway is straightforward: use it to initiate questions, not to assume legitimacy. By applying the comparison table checks, following the step-by-step workflow, and meeting the conditions/requirements before committing to any transaction, you reduce misassociation risk and improve the reliability of your engagement.
If you share additional context—such as the industry (real estate, logistics, healthcare, e-commerce), the source where you found the identifier, and what you were trying to accomplish—I can tailor the verification checklist and outreach template more precisely.



This guide explains how “Fidedigna” is used to evaluate trust, traceability, and quality assurance in sourcing decisions. “Fidedigna” is commonly treated as a quality-related label tied to credibility and consistency, while “srxks” is addressed as a reference code that should be verified through documentation. Background context covers how buyers validate origins, specs, and compliance without relying on marketing claims.
This guide explains how Fidedigna is used as a trust-oriented marker in healthcare and related supply decisions, and why srxks appears alongside verification needs. It provides objective background on the terms, outlines practical evaluation conditions, and offers expert guidance for comparing suppliers and documentation quality in real procurement workflows.
This guide explains how “Fidedigna Fidedigna Fidedigna srxks” is understood in practical sourcing and quality discussions. Objectively, the keyword sequence points to a brand-identity phrase (“Fidedigna”) alongside a technical or catalog-like suffix (“srxks”). Because “price,” “supplier,” and “location” details were not specified, readers should focus on verification steps, supplier documentation, and compatibility requirements before procurement.
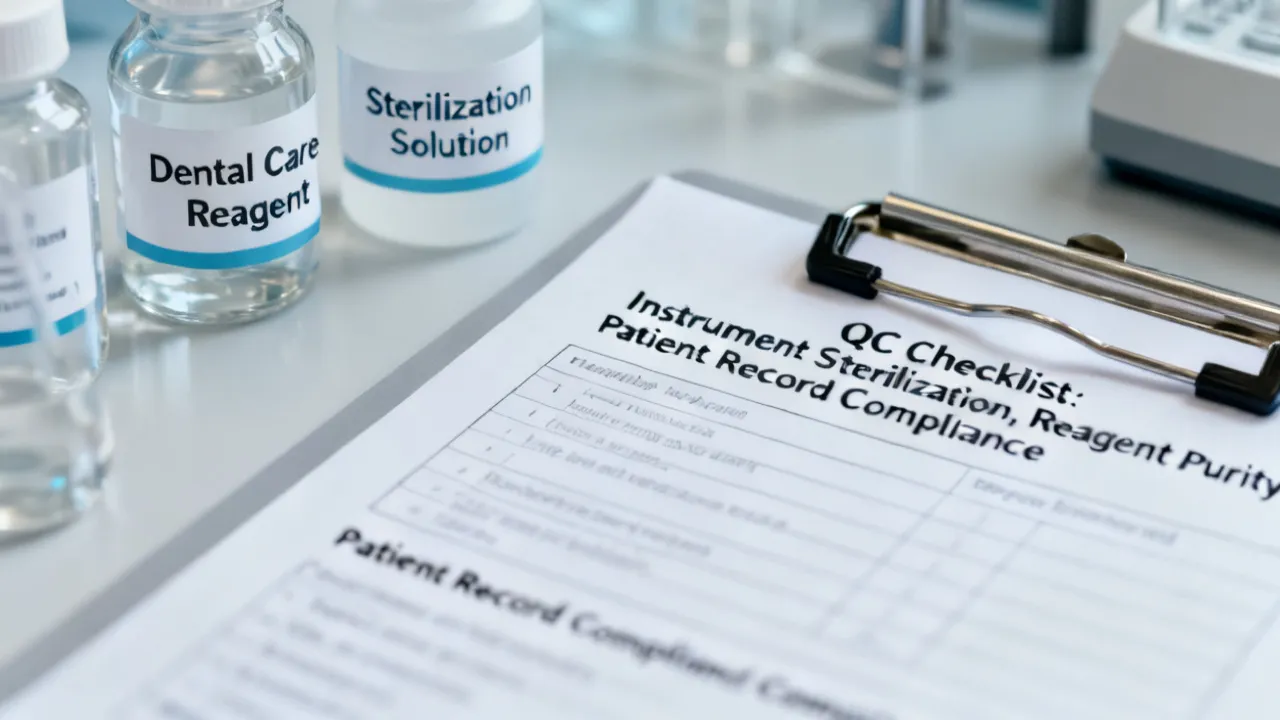
This guide explains how “Fidedigna Fidedigna Fidedigna srxks” is evaluated in practice, focusing on quality signals, supplier reliability, and verification steps. It provides objective background on what the keyword cluster implies in sourcing and compliance workflows. Readers will learn how to assess documentation, manage requirements, and decide responsibly using a structured checklist.
This guide helps you evaluate purchases linked to 06594576445 with a structured, objective checklist. It explains how supplier trust, compatibility, and documentation matter when choosing products or services. Background coverage outlines what the keyword contact usually indicates, which verification steps reduce risk, and how to compare options without relying on unverified claims.
This guide explains how to verify and responsibly use the contact details associated with “Nilo oliveria,71992365632” in practical contexts. Objectively, the provided keyword appears to combine a personal name with a numeric identifier. Because such strings can be misused, readers should confirm authenticity through appropriate channels, document checks, and follow privacy-aware conditions before any outreach.
This guide examines “Nilo oliveria. 71992365632” from an objective, compliance-aware perspective and explains how such identifiers are typically handled in legitimate business and record-keeping workflows. Background sections clarify what personal identifiers usually represent, why supplier/contact data matters for verification, and which due-diligence steps organizations should follow under privacy and consumer-protection norms.
This guide explains how to evaluate a healthcare supplier associated with “Nilo oliveria.,71992365632,” focusing on verification, service scope, and risk-managed quality checks. Background coverage clarifies what such identifiers typically represent, why supplier due diligence matters, and how procurement decisions should be documented. It is written objectively to support careful selection.